Skip to content
Phalanx
roRequest a quote
Menu+

SOC + GRC

Security and compliance in one console.

Start with external scans or a compliance package. Add monitoring when you need alerts and agents. Compliance modules keep policies and evidence linked to controls.

01 / Signal02 / Control03 / Evidence
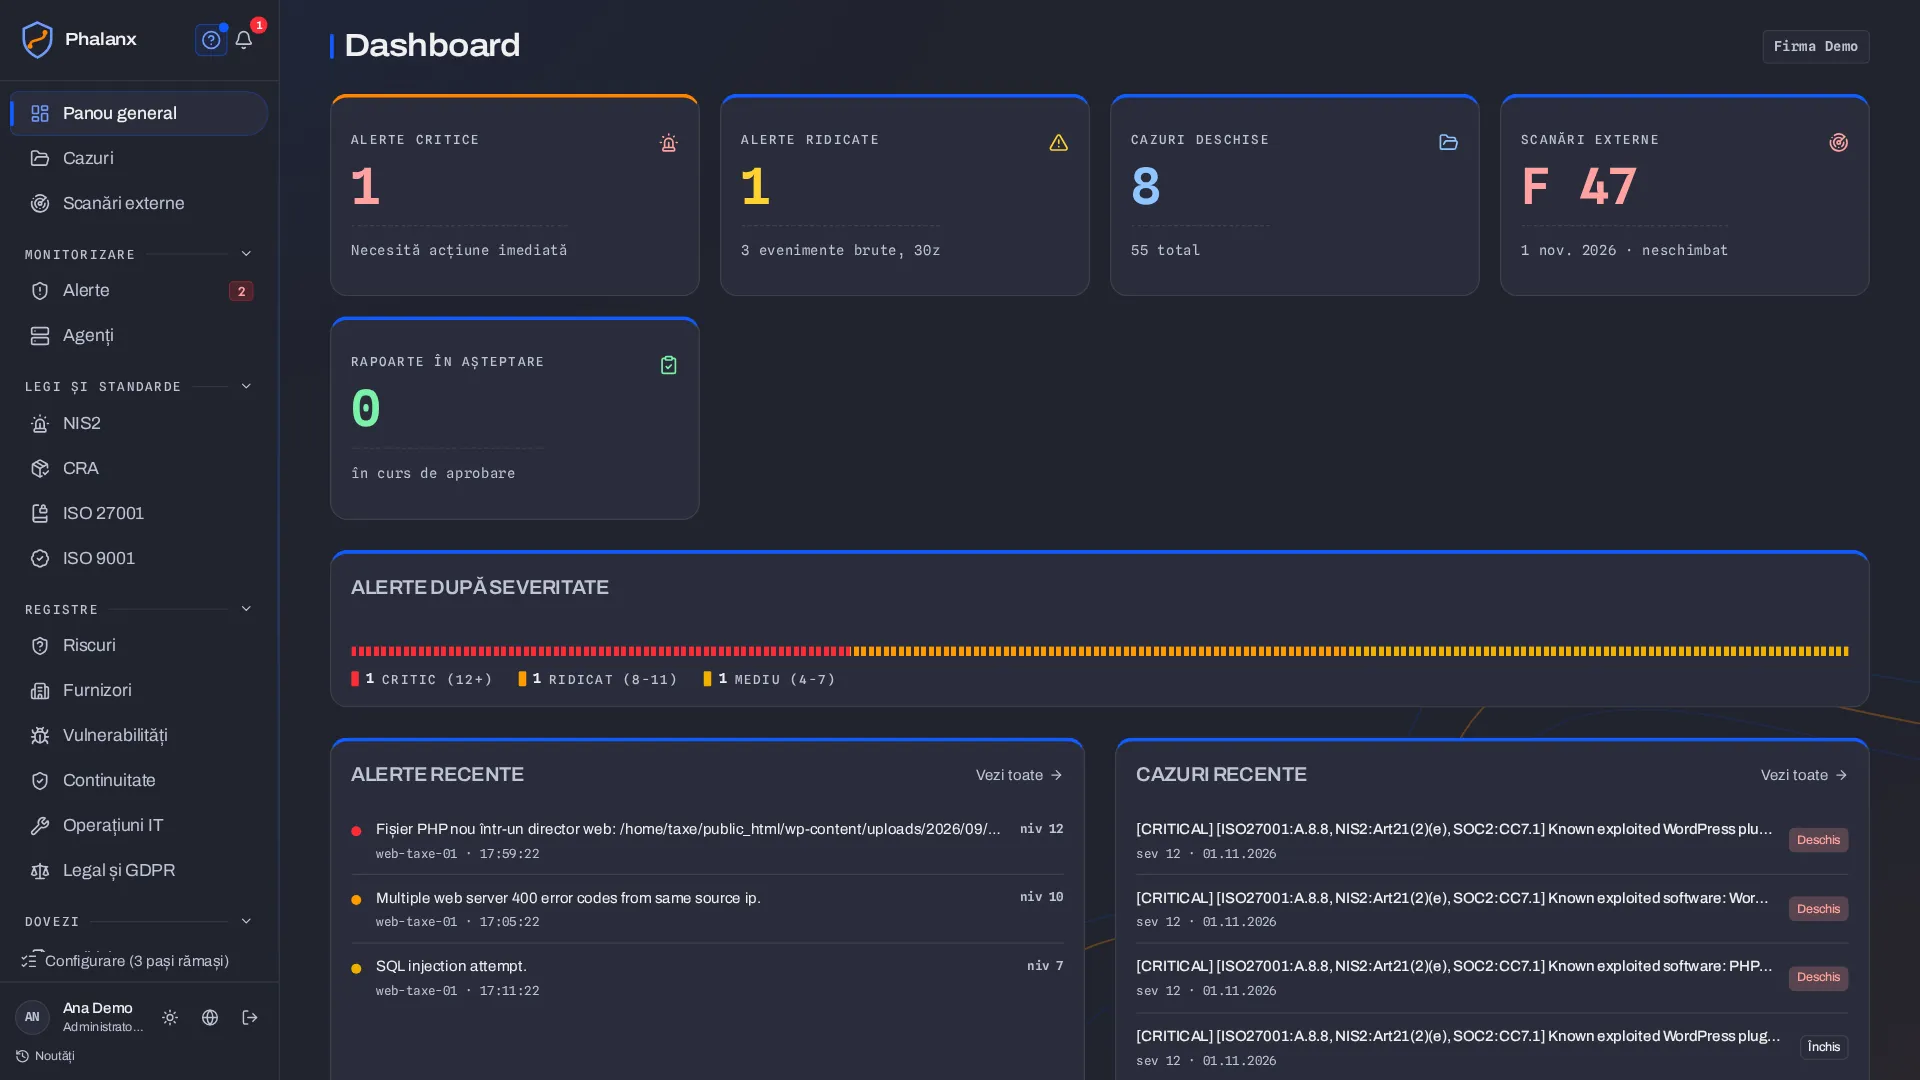
Overview: information from enabled modules.

Where to start

01

I run security for other companies

Run a SOC for your clients. Without running a SOC.

One platform, many clients. Each sees only their own data. Your team sees all of it, from one screen.

  • Alerts arrive filtered to the frameworks each client actually runs
  • Each client's own name and mark, in their console and on exported documents
  • One login for your team, however many clients you carry
See how it works
02

I need to prove compliance

ISO 27001 without the consultant hours.

Your policy set arrives drafted and you approve it. Evidence accumulates as you work, not in the week before the audit.

  • Policies drafted for the controls you are missing, approved by a human
  • Analysis that separates what exists, what is missing and what you cannot prove
  • NIS2 and CRA deadlines counted in the platform, not in a calendar somewhere
See what it covers

Coverage

What it covers today

ISO 27001 and ISO 9001 have separate pages. NIS2 and CRA have their own registers and deadlines, with links to existing ISO controls.

ISO 27001Annex A and clauses 4 to 10All 93 controls plus the 27 management system requirements, each with a document, an approval and an audit log entry.
NIS2Article 21, points a to jArticle 21 maps to ISO controls. The incident register tracks reporting deadlines, and obligations towards DNSC have their own calendar.
CRARegulation (EU) 2024/2847Scope determination, the four reporting deadlines, SBOM ingestion, and Annex I laid over your ISO controls.
ISO 9001Quality management systemA separate quality management page, with the 2015 or 2026 edition and a transition preview. Corrective actions and training records sit alongside the standard’s requirements.
SOC 2Trust Services CriteriaFindings with SOC 2 references show the criterion they support. With Monitoring, you can filter alerts by criteria. Evidence attaches to the audit report according to enabled modules.
GDPRIncluding Romanian Law 190/2018Processing register and evidence workflow, with policies drafted in the right legal context.

Architecture

Open source components, pinned versions, no proprietary lock in.

Nothing running here ties you to us, and the self hosted option gets exactly the same components. We go through the full list in the technical evaluation rather than on a marketing page.

Detection
Event collection, agents, rules
Identity
Authentication, roles and permissions
Storage
Evidence files
API
Platform services
Console
The web interface

Let us find out whether this fits.

Tell us which sites you want to scan or which compliance requirements you have. For client services or self hosting, briefly describe your intended setup.

Request a quote